
 Cyber Strategy
 Cyber Secure
 Cyber Operations
 Cyber Response
 Cyber Resilience
Saudi Arabia has extended its cybersecurity expectations deeper into the private sector. With the Non-CNI Private Sector Entities Cybersecurity Controls, NCNICC-1:2025, the National Cybersecurity Authority has created a minimum cybersecurity baseline for designated private enterprises that do not operate Critical National Infrastructure.
For Saudi businesses, the immediate task is not to buy more security tools. It is to determine whether NCNICC applies, identify the correct entity category, map existing controls against the requirements, and prove that those controls work. DTS Solution in Saudi Arabia supports enterprises through this process with regulatory gap assessments, cybersecurity governance, technical validation, remediation planning, and ongoing compliance support.
The official NCA document makes an important distinction: NCNICC applies to small, medium, and large non-CNI private-sector entities in the Kingdom that are designated by the Authority. Organizations outside its formal scope are still encouraged to use the controls as a cybersecurity baseline.
NCNICC Is Not ECC With a Different Name
Saudi organizations already familiar with the NCA Essential Cybersecurity Controls may assume NCNICC is simply a lighter version of ECC. The relationship is more specific.
NCNICC was developed using the Essential Cybersecurity Controls as a foundation, but its scope is designed for private-sector entities without Critical National Infrastructure. The controls establish a minimum level of cybersecurity suited to different sizes of private enterprise.
That distinction matters when determining compliance. A company should establish which NCA framework applies before it starts mapping controls. A private organization operating CNI, for example, may fall under a different regulatory baseline.
The authoritative reference should always remain the NCA-published NCNICC-1:2025 document. The Authority also states that entities within scope must maintain ongoing compliance and may be assessed using mechanisms determined by the NCA.
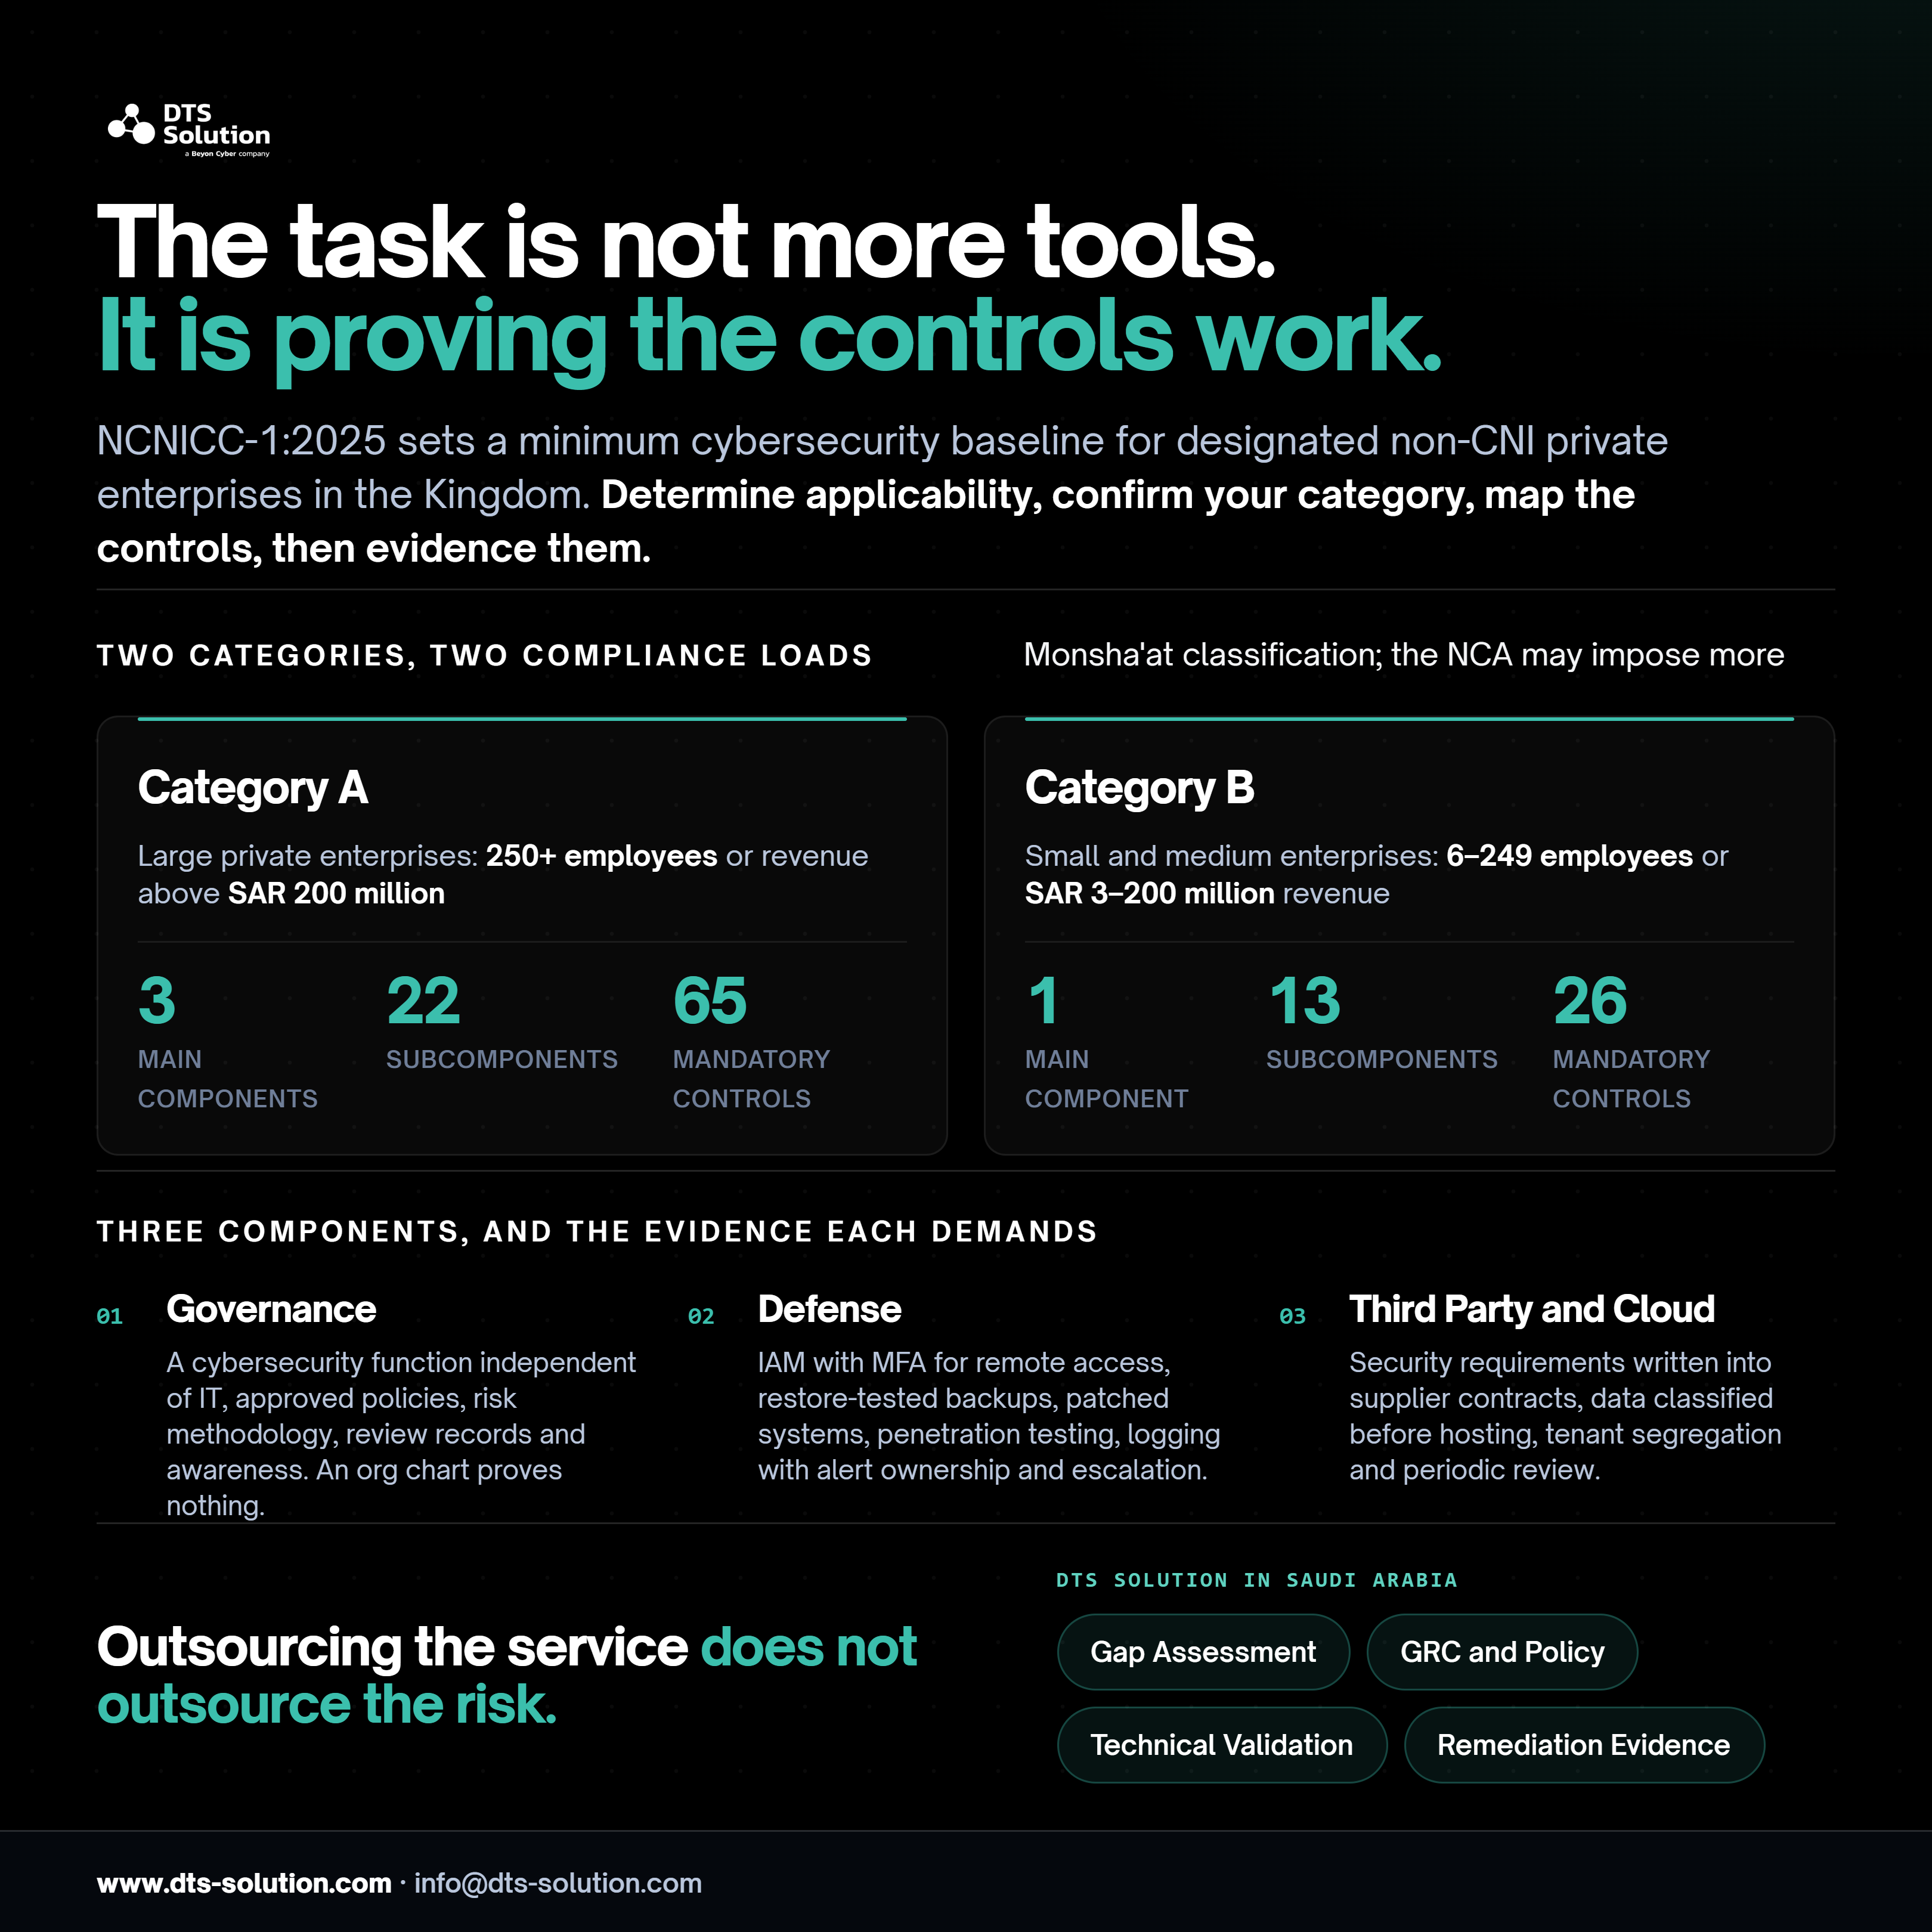
Category A and Category B: The Compliance Load Is Different
NCNICC does not impose the same mandatory control set on every organization.
Category | Entity profile | Mandatory baseline |
Category A | Large private enterprises: more than 250 full-time employees or annual revenue above SAR 200 million | 3 main components, 22 subcomponents and 65 mandatory main controls |
Category B | Small and medium enterprises: 6–249 full-time employees or SAR 3–200 million in annual revenue | 1 main component, 13 subcomponents and 26 mandatory main controls |
The framework uses the Monsha’at classification model and allows the NCA to impose additional controls where required.
For Category A organizations, compliance reaches much further into governance and third-party oversight. Category B has a smaller mandatory baseline, with many governance and supplier-related requirements marked as recommended rather than compulsory.
That does not mean SMEs can ignore those areas. A smaller company using cloud infrastructure, outsourced IT, payment platforms, customer data, or remote access may still carry material exposure even where a control is recommended.
The Three Areas Enterprises Need to Get Right
Detection and response are equally important once an organization moves beyond preventative security.
Through HawkEye Managed CSOC and XDR, DTS Solution provides 24/7 cybersecurity monitoring, threat detection, investigation, threat hunting and incident response capabilities.
Organizations looking for Managed SOC services in Kuwait can use HawkEye to extend their internal security operations with continuous monitoring and specialist response capabilities without having to build every SOC function internally.
HawkEye combines experienced security analysts with automation and AI-assisted capabilities designed to reduce investigation time and help security teams move from alerts to actionable security decisions faster.
Our approach connects Managed SOC operations with incident response, threat hunting and wider cyber resilience services in Kuwait, giving security teams greater visibility across the stages of an attack.
Cybersecurity Defense
This is where NCNICC becomes highly operational.
The framework covers asset management, identity and access management, endpoint protection, email security, network security, mobile devices, data protection, cryptography, backups, vulnerability management, penetration testing, security logging, incident management, physical security, and web application protection.
For example, NCNICC requires identity and access requirements to be defined and implemented, with MFA included for remote access scenarios such as email and external applications.
Backup controls also require more than having a backup product. Organizations must perform recurring backups for critical systems and periodically verify that those backups can be restored.
Vulnerability management follows the same principle: systems must be patched, vulnerabilities identified, and findings treated. Penetration testing is also part of the framework, particularly for Category A entities.
DTS Solution Security Assessments can support the technical evidence behind these requirements through vulnerability assessment, penetration testing, infrastructure review, application testing, and security control validation. DTS also works with Saudi organizations to turn testing results into remediation evidence rather than leaving findings in a final report.
Logging and Incident Response Need Operational Proof
NCNICC expects organizations to collect and monitor cybersecurity event logs so suspicious activity can be identified and investigated. Incident management requirements also cover response procedures, escalation, reporting incidents to the NCA, and sharing relevant cybersecurity information with the Authority.
This makes SOC capability important. A policy that says “security events are monitored” carries little value if the organization cannot show log coverage, alert ownership, escalation records, retention, investigation history, and response procedures.
DTS Solution Security Intelligence Operations supports areas such as NG-SIEM, XDR, threat hunting, attack-surface monitoring, vulnerability management, and incident detection, all of which can support a stronger operational control environment. (DTS)
Third Parties and Cloud Cannot Sit Outside Compliance
NCNICC also addresses outsourced technology, managed services, supplier contracts, cloud computing, and hosting.
For relevant controls, organizations need cybersecurity requirements built into supplier agreements, including confidentiality expectations and incident communication procedures. Cloud controls cover areas such as data classification before hosting, segregation of the organization’s environment from other tenants, documented requirements, implementation, and periodic review.
This is an important point for Saudi enterprises using regional or global technology providers: outsourcing the service does not remove the organization’s responsibility for the risk.
What NCNICC Readiness Should Look Like
A useful NCNICC program starts with applicability and category determination. From there, the organization should build a control-level gap assessment that distinguishes mandatory requirements from recommendations.
Each applicable control should then have an owner, implementation status, evidence source, identified gap, remediation action, and target date. Technical requirements should be validated through testing rather than accepted only from policies.
The final objective is continuous readiness. NCNICC requires ongoing compliance, while the NCA retains responsibility for periodically reviewing and updating the controls.
Saudi Arabia has extended its cybersecurity expectations deeper into the private sector. With the Non-CNI Private Sector Entities Cybersecurity Controls, NCNICC-1:2025, the National Cybersecurity Authority has created a minimum cybersecurity baseline for designated private enterprises that do not operate Critical National Infrastructure.
For Saudi businesses, the immediate task is not to buy more security tools. It is to determine whether NCNICC applies, identify the correct entity category, map existing controls against the requirements, and prove that those controls work. DTS Solution in Saudi Arabia supports enterprises through this process with regulatory gap assessments, cybersecurity governance, technical validation, remediation planning, and ongoing compliance support.
The official NCA document makes an important distinction: NCNICC applies to small, medium, and large non-CNI private-sector entities in the Kingdom that are designated by the Authority. Organizations outside its formal scope are still encouraged to use the controls as a cybersecurity baseline.
NCNICC Is Not ECC With a Different Name
Saudi organizations already familiar with the NCA Essential Cybersecurity Controls may assume NCNICC is simply a lighter version of ECC. The relationship is more specific.
NCNICC was developed using the Essential Cybersecurity Controls as a foundation, but its scope is designed for private-sector entities without Critical National Infrastructure. The controls establish a minimum level of cybersecurity suited to different sizes of private enterprise.
That distinction matters when determining compliance. A company should establish which NCA framework applies before it starts mapping controls. A private organization operating CNI, for example, may fall under a different regulatory baseline.
The authoritative reference should always remain the NCA-published NCNICC-1:2025 document. The Authority also states that entities within scope must maintain ongoing compliance and may be assessed using mechanisms determined by the NCA.
Category A and Category B: The Compliance Load Is Different
NCNICC does not impose the same mandatory control set on every organization.
Category | Entity profile | Mandatory baseline |
Category A | Large private enterprises: more than 250 full-time employees or annual revenue above SAR 200 million | 3 main components, 22 subcomponents and 65 mandatory main controls |
Category B | Small and medium enterprises: 6–249 full-time employees or SAR 3–200 million in annual revenue | 1 main component, 13 subcomponents and 26 mandatory main controls |
The framework uses the Monsha’at classification model and allows the NCA to impose additional controls where required.
For Category A organizations, compliance reaches much further into governance and third-party oversight. Category B has a smaller mandatory baseline, with many governance and supplier-related requirements marked as recommended rather than compulsory.
That does not mean SMEs can ignore those areas. A smaller company using cloud infrastructure, outsourced IT, payment platforms, customer data, or remote access may still carry material exposure even where a control is recommended.
The Three Areas Enterprises Need to Get Right
NCNICC is structured around three main components: Cybersecurity Governance, Cybersecurity Defense, and Third-Party and Cloud Computing Cybersecurity.
Cybersecurity Governance
For larger enterprises, NCNICC expects cybersecurity to have formal ownership. The framework addresses cybersecurity management, approved policies, risk management, periodic review, independent assessment, and employee awareness.
Category A organizations should pay close attention to organizational independence. The controls call for a cybersecurity administrative function that is independent from IT, supported by defined responsibilities and qualified personnel.
The practical issue is evidence: an organizational chart alone will not prove governance. Enterprises need approved policies, risk methodology, review records, management decisions, awareness records, control owners, and evidence that cybersecurity requirements are being applied.
This is where DTS Solution Governance, Risk and Compliance can support policy development, risk assessment, control mapping, compliance reviews, metrics, and remediation governance.
Cybersecurity Defense
This is where NCNICC becomes highly operational.
The framework covers asset management, identity and access management, endpoint protection, email security, network security, mobile devices, data protection, cryptography, backups, vulnerability management, penetration testing, security logging, incident management, physical security, and web application protection.
For example, NCNICC requires identity and access requirements to be defined and implemented, with MFA included for remote access scenarios such as email and external applications.
Backup controls also require more than having a backup product. Organizations must perform recurring backups for critical systems and periodically verify that those backups can be restored.
Vulnerability management follows the same principle: systems must be patched, vulnerabilities identified, and findings treated. Penetration testing is also part of the framework, particularly for Category A entities.
DTS Solution Security Assessments can support the technical evidence behind these requirements through vulnerability assessment, penetration testing, infrastructure review, application testing, and security control validation. DTS also works with Saudi organizations to turn testing results into remediation evidence rather than leaving findings in a final report.
Logging and Incident Response Need Operational Proof
NCNICC expects organizations to collect and monitor cybersecurity event logs so suspicious activity can be identified and investigated. Incident management requirements also cover response procedures, escalation, reporting incidents to the NCA, and sharing relevant cybersecurity information with the Authority.
This makes SOC capability important. A policy that says “security events are monitored” carries little value if the organization cannot show log coverage, alert ownership, escalation records, retention, investigation history, and response procedures.
DTS Solution Security Intelligence Operations supports areas such as NG-SIEM, XDR, threat hunting, attack-surface monitoring, vulnerability management, and incident detection, all of which can support a stronger operational control environment.
Third Parties and Cloud Cannot Sit Outside Compliance
NCNICC also addresses outsourced technology, managed services, supplier contracts, cloud computing, and hosting.
For relevant controls, organizations need cybersecurity requirements built into supplier agreements, including confidentiality expectations and incident communication procedures. Cloud controls cover areas such as data classification before hosting, segregation of the organization’s environment from other tenants, documented requirements, implementation, and periodic review.
This is an important point for Saudi enterprises using regional or global technology providers: outsourcing the service does not remove the organization’s responsibility for the risk.
What NCNICC Readiness Should Look Like
A useful NCNICC program starts with applicability and category determination. From there, the organization should build a control-level gap assessment that distinguishes mandatory requirements from recommendations.
Each applicable control should then have an owner, implementation status, evidence source, identified gap, remediation action, and target date. Technical requirements should be validated through testing rather than accepted only from policies.
The final objective is continuous readiness. NCNICC requires ongoing compliance, while the NCA retains responsibility for periodically reviewing and updating the controls.
Where DTS Solution Fits
For private enterprises in Saudi Arabia, DTS Solution can support the full NCNICC readiness cycle: applicability review, gap assessment, control mapping, policy and governance development, technical assessments, remediation validation, and evidence preparation.
The value is practical: determine what applies, identify what is missing, test whether the controls work, and build evidence that can survive regulatory review.
See also:


 Dubai
